Quick Answer
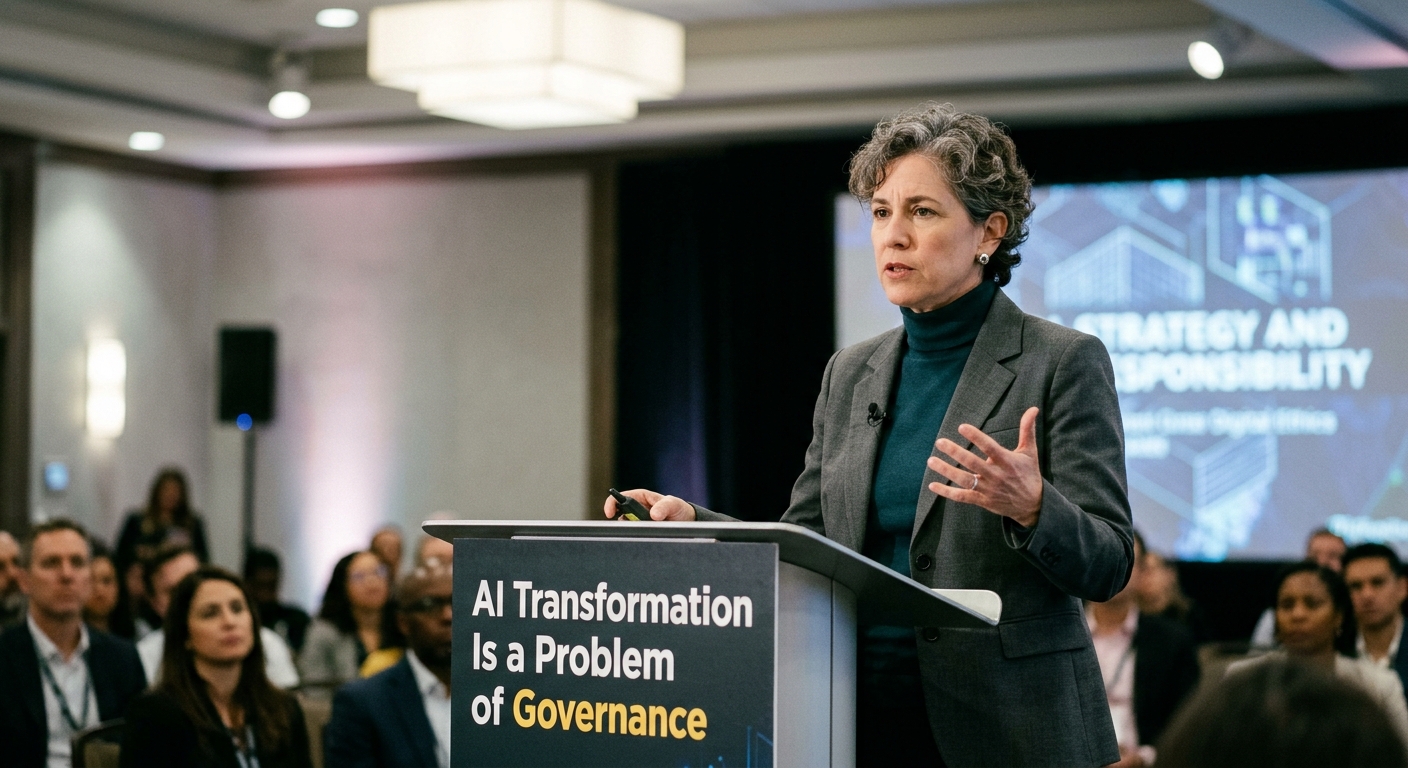
AI transformation is a problem of governance when organizations adopt AI faster than they establish clear ownership, accountability, data protection, and oversight. Buying advanced AI software does not automatically improve business operations. Organizations need defined responsibilities, risk controls, human supervision, and measurable performance standards to turn AI experiments into reliable business systems.
Artificial intelligence is changing how businesses handle information, serve customers, analyze data, and make decisions. However, many organizations still struggle to turn individual AI projects into meaningful operational improvements.
The issue is often not the technology itself. It is the lack of organizational structures needed to manage AI responsibly. Understanding this difference helps business leaders move beyond experimenting with AI and build systems that deliver measurable results.
Why Is AI Transformation a Problem of Governance?
AI transformation requires more than introducing new software into existing workflows. It changes how employees work, how information moves between departments, and how business decisions are made.
Without proper governance, organizations can end up with disconnected AI tools, unclear responsibilities, inconsistent security practices, and systems that produce results nobody knows how to verify.
Consider a company that introduces generative AI across its marketing, customer support, and finance departments. Each department selects different tools, uploads information, and creates its own working procedures.
Initially, productivity may improve. However, problems emerge when employees use confidential information in unapproved applications, AI-generated recommendations contain errors, or departments cannot explain how important decisions were reached.
These problems are not necessarily caused by weak AI models. They reflect a failure to establish consistent rules for using the technology.
This is why AI governance must become part of the transformation strategy rather than an administrative task added after implementation.
The Difference Between AI Adoption and AI Transformation
AI adoption means introducing artificial intelligence into a particular activity or business process. AI transformation goes further by changing how an organization operates around the technology.
| AI Adoption | AI Transformation |
|---|---|
| Introducing AI applications | Redesigning business workflows |
| Automating individual tasks | Improving complete processes |
| Allowing teams to experiment | Establishing shared standards |
| Measuring tool usage | Measuring business outcomes |
| Managing projects individually | Coordinating organization-wide AI |
| Focusing on technology | Balancing technology, people, and governance |
For example, using an AI writing assistant to prepare marketing content represents AI adoption. Building a controlled content workflow with approved data sources, editorial review, accountability, and performance measurement represents a more mature approach to AI transformation.
The distinction matters because successful AI transformation requires changes to the organization, not simply a larger collection of software subscriptions.
What Happens When AI Governance Falls Behind?
Poor governance creates problems that can affect productivity, customer confidence, business operations, and regulatory compliance.
Several issues become particularly important as AI moves into everyday workflows.
1. Nobody Takes Responsibility for AI Decisions
AI systems can generate recommendations, summarize information, classify requests, and perform automated tasks. However, someone must remain responsible for how those outputs are used.
Without clear ownership, employees may assume that another department checks AI-generated information. Technical teams may believe business managers are responsible, while managers expect software providers to handle every risk.
This creates accountability gaps.
Organizations should assign a business owner to each important AI application. That person should understand its purpose, approve its use, monitor performance, and know when the system needs human intervention.
2. Sensitive Business Information Can Be Exposed
Employees frequently use AI assistants to summarize documents, analyze spreadsheets, draft emails, and answer questions.
The convenience can create problems when workers upload confidential information to applications that have not been approved by their organization.
A company may have several AI subscriptions without knowing:
-
Which applications process business information.
-
What data employees are allowed to upload.
-
Who can access stored information.
-
How long information is retained.
-
Whether vendors use submitted data for additional purposes.
A governance framework should establish clear data-handling rules before employees receive access to AI applications.
Organizations should also review vendor privacy policies, contractual protections, access controls, and available data-retention settings.
3. AI Outputs Can Influence Decisions Without Proper Review
AI-generated information can appear convincing even when it contains inaccurate or incomplete details.
This becomes a serious business concern when employees rely on AI recommendations for financial analysis, recruitment, customer communication, or other important activities.
Human oversight should reflect the consequences of an incorrect output.
For example, an AI assistant that suggests alternative email subject lines may need only routine editorial review. A system that influences an important customer decision requires stronger controls, documented checks, and a clearly responsible person.
4. Different Departments Follow Different AI Rules
When individual departments introduce their own AI tools, organizations can develop inconsistent practices.
One department may review every AI-generated report, while another may publish content without checking its accuracy. Some teams may use approved applications, while others rely on personal accounts.
A shared governance framework helps establish consistent requirements without preventing departments from choosing tools that suit their work.
What Does Effective AI Governance Actually Include?
AI governance is the combination of policies, responsibilities, technical controls, and monitoring processes that guide how an organization develops, purchases, and uses artificial intelligence.
It should cover the entire AI lifecycle, from selecting a tool to reviewing its performance and eventually retiring it.
The National Institute of Standards and Technology (NIST) provides a useful reference through its AI Risk Management Framework. It organizes AI risk management around four connected functions: Govern, Map, Measure, and Manage.
1. Clear Ownership and Accountability
Every important AI system should have a clearly identified owner.
This does not mean one person must manage every technical detail. Instead, responsibilities should be distributed across the people who understand business operations, technology, security, and compliance.
A practical ownership structure might include:
-
Executive leadership: Sets AI priorities and approves the organization’s risk tolerance.
-
Business owners: Define the purpose of AI applications and remain responsible for business outcomes.
-
IT and security teams: Manage technical access, infrastructure, and security requirements.
-
Legal and compliance teams: Review relevant legal obligations and contractual risks.
-
Employees: Follow approved procedures and report problems.
The goal is to prevent important decisions from falling between departments.
2. Risk Classification Before Deployment
Not every AI application creates the same level of risk.
An AI tool used to organize public information does not require the same oversight as a system that influences employment, financial decisions, or access to important services.
Organizations should classify AI applications according to their intended use, data access, potential impact, and level of autonomy.
A simple internal classification can help:
| Risk Level | Example | Governance Requirement |
|---|---|---|
| Low | Drafting internal meeting notes | Basic usage rules |
| Moderate | Customer support assistance | Output review and data controls |
| High | Important decisions affecting individuals | Strong testing, documented oversight, and approval |
This is an illustrative business classification, not an official NIST or EU legal risk classification.
The European Commission’s AI Act framework also uses a risk-based approach. Its requirements depend on the type of AI system, the role of the organization, and the intended application. Businesses should consult the official European Commission AI Act guidance when assessing relevant obligations.
3. Data Protection and Access Controls
AI governance should define what information an application can access and how that information can be used.
This becomes especially important when organizations introduce AI agents that can interact with documents, databases, business applications, and other connected systems.
For example, an AI assistant designed to summarize customer support conversations should not automatically receive permission to access employee payroll records.
A sensible approach includes:
-
Granting access only to information required for the task.
-
Using approved AI applications for business information.
-
Separating personal and organizational accounts.
-
Reviewing vendor data-processing terms.
-
Maintaining appropriate access logs.
-
Removing permissions when they are no longer required.
These controls reduce unnecessary exposure while allowing employees to use AI productively.
4. Human Oversight and Performance Monitoring
Governance should continue after an AI application becomes operational.
Organizations need procedures for checking accuracy, identifying unexpected behaviour, investigating complaints, and responding to security or operational incidents.
Human oversight does not mean employees must manually approve every AI-generated sentence. That would remove much of the efficiency that automation is supposed to provide.
Instead, the level of review should reflect the possible consequences of an error.
The OECD AI Principles emphasize accountability, transparency, human agency, and ongoing risk management throughout the AI system lifecycle.
5. Documented Policies and Incident Procedures
A governance policy should explain what employees can do, what requires approval, and what happens when something goes wrong.
For example, employees should know how to report inaccurate AI outputs, unauthorized data access, unexpected automated actions, or other problems.
Organizations also need a process for suspending an application when its risks become unacceptable.
Without documented procedures, teams may respond differently to the same problem. That makes it harder to investigate incidents and prevent similar issues in the future.
How Can Businesses Build an AI Governance Framework?
A practical governance framework does not need to begin with a large compliance department or expensive enterprise software.
Businesses can start by understanding their existing AI usage and gradually introduce controls based on the risks involved.
The following steps provide a useful starting point.
Step 1: Create an Inventory of AI Tools
Identify the AI applications currently used across the organization.
Include officially approved software, department-specific subscriptions, and applications employees use independently for work.
For each application, record:
-
Its business purpose.
-
The department using it.
-
The information it can access.
-
The responsible business owner.
-
Whether it connects to other systems.
-
Any known security or compliance concerns.
This inventory gives management a clearer picture of actual AI adoption.
Step 2: Define Acceptable Usage Rules
Establish clear guidelines explaining which AI applications employees can use and what information they can submit.
For example, an organization may permit employees to use an approved AI assistant for public research while restricting the upload of confidential customer records.
These rules should be easy to understand and accessible to employees.
A policy that exists only in a lengthy document is unlikely to influence everyday behaviour.
Step 3: Assign Decision-Making Authority
Decide who can approve new AI applications, authorize access to sensitive information, and accept specific business risks.
The organization should also establish who can suspend an AI system when it produces unreliable results or violates internal requirements.
This prevents teams from introducing important changes without the necessary approval.
Step 4: Test Applications Before Wider Deployment
Before expanding an AI tool across the organization, evaluate whether it performs its intended task reliably.
Testing should cover accuracy, privacy, security, consistency, and the system’s behaviour under unexpected conditions.
Businesses should also test how an AI application interacts with existing software and workflows.
A successful demonstration does not automatically prove that a system is ready for everyday business use.
Step 5: Monitor Results and Review Permissions
After deployment, measure performance regularly and review whether access permissions remain appropriate.
Monitor issues such as inaccurate outputs, unexpected costs, employee adoption, security incidents, and changes in business requirements.
Governance should evolve as the application, its users, and the surrounding risks change.
Step 6: Train Employees and Update Procedures
Employees need to understand both the benefits and limitations of the AI tools they use.
Training should explain how to verify important outputs, protect business information, identify unreliable results, and report incidents.
Management should review policies when applications introduce new capabilities, particularly when AI systems gain access to additional business functions or autonomous actions.
Why AI Agents Make Governance More Important
Traditional AI assistants generally respond to user instructions. More advanced AI agents can perform multiple connected tasks, interact with applications, retrieve information, and execute actions within authorized environments.
This changes the governance challenge.
An AI agent connected to a customer relationship management system, for example, might retrieve customer records, prepare recommendations, and update selected information.
The organization must decide which actions the agent can perform independently and which require human approval.
Important questions include:
-
Which applications can the agent access?
-
Can it modify or delete business information?
-
What actions require approval?
-
Can its activities be reviewed afterward?
-
Who is responsible if an automated action creates a problem?
-
How can access be suspended?
Permission controls should match the agent’s responsibilities. An agent that summarizes information does not need the same access as one authorized to modify business records.
McKinsey’s recent research on organizational AI transformation also emphasizes the importance of clear authority, shared infrastructure, evaluation, permissions, and lifecycle management when organizations move toward agent-based operations.
The important lesson is that increasing AI autonomy should be accompanied by stronger operational controls, not simply greater trust in the technology.
How Do You Measure Whether AI Governance Is Working?
Organizations should not measure AI governance only by the number of policies they publish or applications they approve.
The real test is whether those controls improve the reliability, accountability, and business value of AI systems.
Several indicators can help:
| Measurement | What It Reveals |
|---|---|
| Approved AI applications | Whether tools are properly reviewed |
| Assigned system owners | Whether accountability is established |
| Access reviews | Whether permissions remain appropriate |
| AI output accuracy | Whether systems perform reliably |
| Incident response time | Whether problems are handled effectively |
| Employee training completion | Whether users understand AI policies |
| Business process improvements | Whether AI creates measurable value |
| Ongoing risk reviews | Whether governance adapts to change |
These indicators should be selected according to the organization’s size, industry, and AI use cases.
For instance, a business using AI mainly for internal content creation may focus on accuracy, employee training, and data protection. A company using AI in important customer decisions will need stronger monitoring, documentation, and human oversight.
The objective is to connect governance activities with actual business performance.
Is AI Governance More Important Than AI Technology?
Neither can replace the other.
Technology determines what an AI system can do, while governance determines how an organization should use it, who is responsible, and what safeguards are necessary.
An organization with excellent governance but unsuitable technology may struggle to achieve its objectives. Similarly, an organization with advanced AI software but weak oversight may introduce unnecessary risks.
Successful transformation requires both.
Business leaders should also avoid treating governance as a reason to delay every AI project. Excessive approval requirements can slow experimentation and discourage employees from exploring useful applications.
The better approach is proportional governance: apply controls according to the potential impact of each system.
Low-risk applications can follow simpler approval procedures, while applications involving sensitive information or important decisions require stronger evaluation and oversight.
This allows businesses to encourage innovation without losing control of their operations.
Final Thoughts
AI transformation is a problem of governance when organizations focus on adopting technology without preparing the structures needed to manage it.
The strongest AI strategy is not necessarily the one with the largest number of applications or the most advanced models. It is the one that connects technology with clear ownership, responsible data practices, human oversight, and measurable business objectives.
Organizations should begin by identifying the AI tools they already use, assigning responsibility, and establishing practical rules for their deployment.
As AI becomes more integrated into everyday operations, governance will become an essential part of making that technology useful, accountable, and sustainable.
Frequently Asked Questions
What does AI transformation is a problem of governance mean?
It means organizations often struggle to scale AI because their responsibilities, policies, and oversight processes have not developed as quickly as their technology adoption. Successful transformation requires clear ownership, risk management, and accountability alongside technical improvements.
Why does AI transformation fail without governance?
Without governance, businesses can experience inconsistent AI usage, data protection problems, unreliable outputs, and unclear responsibility for automated decisions. These issues make it difficult to trust AI systems or introduce them across different departments.
What are the four functions of the NIST AI Risk Management Framework?
NIST’s AI Risk Management Framework identifies four functions: Govern, Map, Measure, and Manage. Together, they help organizations establish oversight, understand risks, evaluate AI systems, and respond to identified problems throughout their lifecycle.
Who should be responsible for AI governance in a company?
AI governance should involve executive leadership, business owners, IT and security teams, and legal or compliance professionals. A designated leadership structure should establish responsibilities while individual business owners remain accountable for the outcomes of their AI applications.
How can small businesses implement AI governance?
Small businesses can begin with an inventory of their AI applications, basic data protection rules, approved software, and clearly assigned responsibilities. They can then introduce more detailed testing and monitoring as their AI usage and associated risks increase.